Network
Vulernability Assessment & Penetration Testing
vulnerability assessment and penetration testing
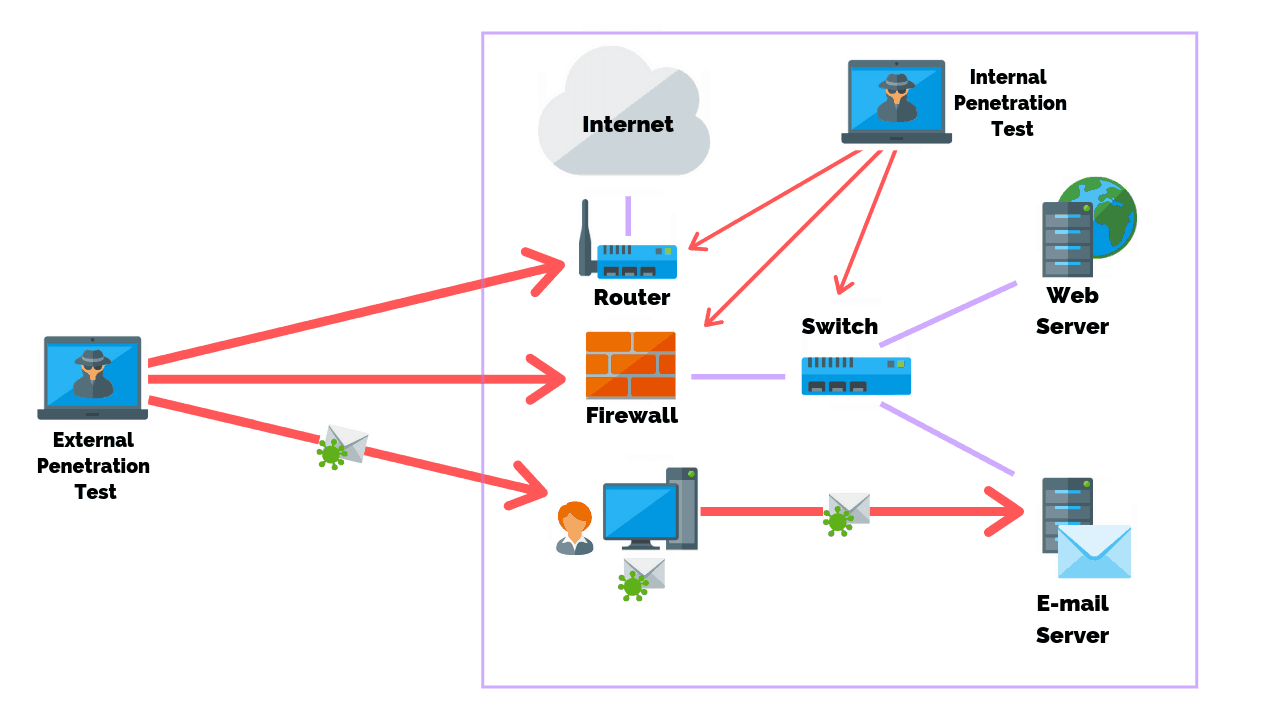
Network VAPT is the assessment procedure that is conducted by our network security experts on the organization's network for identifying possible vulnerabilities that the attackers could exploit. The primary objective of a network penetration test is to recognize exploitable vulnerabilities in desktops, servers, networks, network devices (i.e., switches, routers) and security devices (i.e., firewall, IDS, IPS) before hackers can discover as well as exploit them.
vulnerability assessment
A network vulnerability assessment is a process that helps review and analyze your organization's computer and network for security issues. The assessment may expose network vulnerabilities and holes in your security that could leave an open door for hackers. A network vulnerability assessment should also be performed on an ongoing basis as new threats arise and hackers find additional ways to break into systems.
Identify security flaws present in the environment
Understand the level of risk for your organization
Help address and fix identified network security flaws
Penetration Testing
Once the threats and vulnerabilities have been evaluated, the penetration testing will address the risks identified throughout the environment. The penetration testing will be appropriate for the complexity and size of an organization. The penetration testing will attempt to exploit security vulnerabilities and weaknesses found throughout the environment, attempting to penetrate network.
The goal of penetration testing is to determine if unauthorized access to key systems and files can be achieved. If access is achieved, the vulnerability should be corrected and the penetration testing re-performed until the test is clean and no longer allows unauthorized access or other malicious activity.
Other Services