Security Operation Center
Security Operation Center
A Security Operations Center (SOC) facilitates in detecting and preventing your organization against cyber-attacks executed hackers across the world and hackers existing inside your organization as well. This detection and prevention are achieved through continuous monitoring and analyzing an organization’s incoming and outgoing traffic in the form of logs, which is done by our information security team expertise.
Irrespective of the business scale, it is mandatory for an organization to secure all its personal and customer data. Data security is a must while the data is in transit and stored in the databases. Many organizations, irrespective of their business model, scale, scope or compliance are concerned about protecting their data and their customer's data from hackers. This, in turn, helps the organizations to scale up their credibility and reliability among customers.
Log Monitoring
Monitoring an organisation's network helps in detecting any happenings of suspicious or malicious activities which can be a cyber-attack or any policy violations against the organization. The entire events that are happening within the defined scope or under compliance are monitored 24/7 to ensure that an organization is protected and secured from such activities.
With the help of Security Information and Event Management (SIEM) tool, the monitoring process is made possible to detect cyber threats which can originate from either inside or outside an organization.
Threat detection
Upon the log monitoring, the objective of threat detection is to continuously check each and every log that is being received and detect any anomaly or threat which can be the indicators of an attack (IOA) or indicators of compromise (IOC).Simply, the pro-active measures of finding and stopping the threats from entering into an organization network.
The threat detection is made easier and more accurate by implementing Artificial Intelligence (AI) & Machine Learning (ML), which helps in finding cyber threats and creating an automated alert mechanism for those alerts.
Incident Response
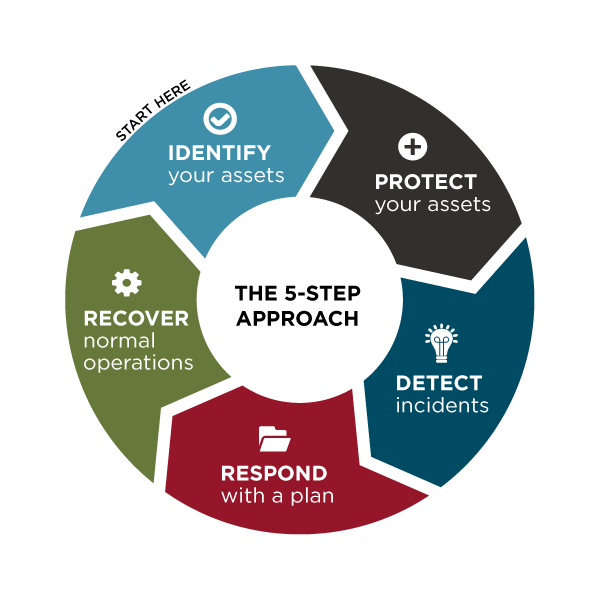
The Incident Response (IR) is an organized approach to address and manage the aftermath of a security breach or cyber-attack. The goal is to handle the situation in a way that minimizes the damage and reduces recovery time and costs, also, to ensure that the issues are addressed immediately upon discovery.
Further, this attack pattern is noted and recoreded using threat intelligence based on the threat's signature or behaviour to mitigate the same kind of attacks in future with ease.
As the cyberattacks increase in scale and frequency, incident response plans become more vital to a company’s cyber defences. Poor incident response can put the organization's assets and data at high risk. Effective incident response is critical, regardless of your industry.
Other Services